ISO/IEC 27001 Lead Auditor Training Audit the ISO/IEC 27001:2022 ISMS edition with confidence
This ISO/IEC 27001 Lead Auditor training is a 40-hour, CQI IRCA certified course on ISO/IEC 27001:2022. It is delivered live online as Virtual Instructor Led Training (VILT). First you plan a certification audit of an information security management system (ISMS). Then you carry it out, from stage 1 to the closing meeting, in line with ISO 19011.
ISO/IEC 27001:2022 ISMS Lead Auditor online training course
ISO 27001 Lead Auditor training is a 40-hour CQI IRCA certified course. It gives you the knowledge and skills to plan, conduct, report and follow up audits of an information security management system (ISMS) against ISO/IEC 27001:2022. In addition, it covers first, second and third-party audits, in accordance with ISO 19011 and ISO/IEC 17021-1.
3FOLD Training is a CQI IRCA Approved Training Partner. CQI and IRCA, UK certify this ISO/IEC 27001 Lead Auditor training under course reference PR373. From the first session, you work as an audit team on the certification audit of a realistic case-study organization, while your trainer plays the auditee.
Delegates who successfully complete this CQI and IRCA Certified ISO/IEC 27001:2022 Lead Auditor (ISMS) training course — within the five years prior to making an application to become a certificated auditor — satisfy the training requirement for initial certification as an IRCA ISMS auditor.
By the end of this course you will be able to
Explain the purpose of information security management system (ISMS) standards, management-system audit and third-party certification, and the business benefits of effective information security management.
Explain the role of an auditor to plan, conduct, report and follow up an ISMS audit, in accordance with ISO 19011 and ISO/IEC 17021-1.
Plan, conduct, report and follow up an audit of an ISMS to establish conformity, or otherwise, with ISO/IEC 27001:2022.
Standard
ISO/IEC 27001:2022 (current edition)
Certified by
CQI and IRCA, UK · PR373
Duration
40 hours
Delivery
100% online VILT on Zoom
Batches
5-Sunday weekend batch
Assessment
Continuous assessment + online exam
Exam
40 questions · 80 marks · 1 h 45 min · open book +30 min if English is not your first language
Fee
AED 2020 / USD 550 incl. VAT and first exam attempt
Who should attend
Information security managers
IT, risk and GRC professionals
Internal auditors
Compliance professionals
Supplier and second-party auditors
ISMS consultants
Certification body auditors
Anyone pursuing IRCA ISMS auditor certification
Expected prior knowledge: a working knowledge of information security management and ISO/IEC 27001. A self-paced ISMS Foundation module and readiness quiz on the 3FOLD LMS bring you up to speed before the live sessions start.
Certified course
Approved by CQI and IRCA, UK
3FOLD Training is a CQI IRCA Approved Training Partner. In addition, CQI and IRCA officially certify this ISO/IEC 27001 ISMS Lead Auditor training course. As a result, employers and certification bodies worldwide recognize your training and your certificate.
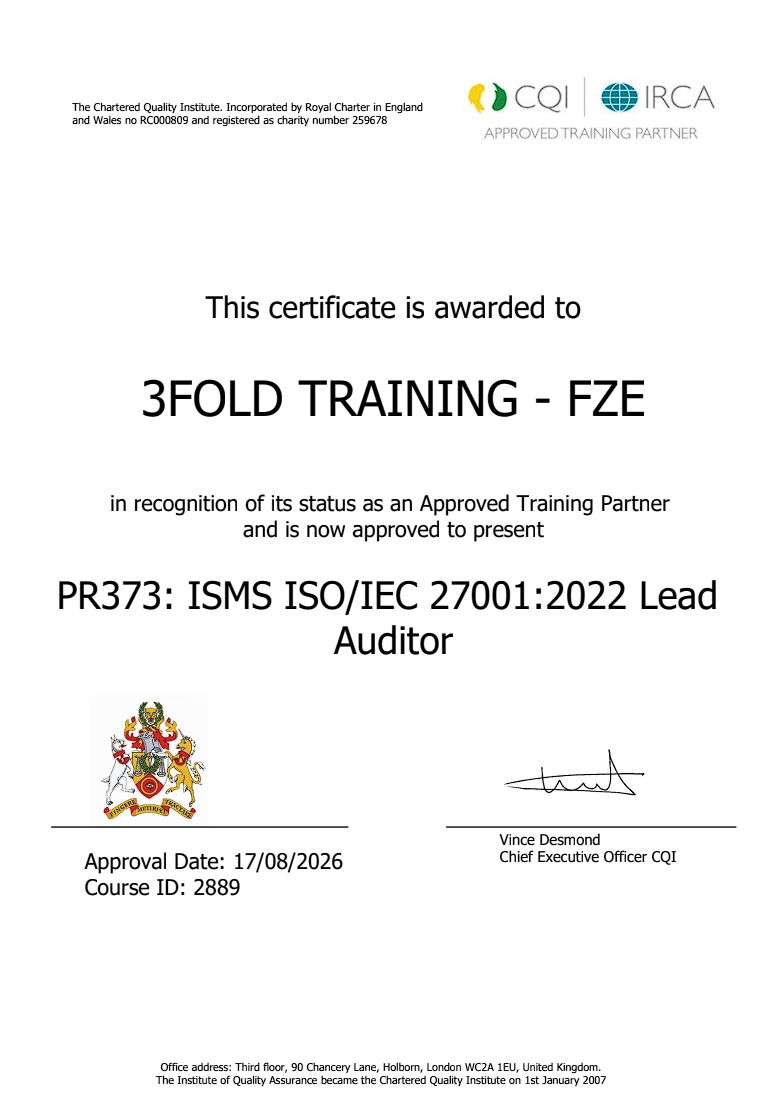
CQI IRCA course certificate PR373. It confirms that CQI IRCA approves 3FOLD Training to present this course.
ISO/IEC 27001:2013 vs ISO/IEC 27001:2022
What changed in ISO/IEC 27001:2022 — and how you will audit it
ISO/IEC 27001:2022 is the current, widely-adopted edition of the ISMS standard. Clauses 4–10 changed only a little, but Annex A was restructured. Select a clause to see what is new and what it means for a lead auditor. Then see where you practice it in this ISO 27001 Lead Auditor training.
New requirementsRestructured or strengthenedClarified
4.2
Clarified
Interested-party requirements now split in two
What changed
Clause 4.2 now separates the interested parties' requirements that are relevant to the ISMS from the subset that the organization chooses to address through the ISMS.
Clauses 4.1, 4.3 and 4.4 stay essentially unchanged.
What it means for the auditor
Check that the organization can show both lists, not just one combined register, and that the Statement of Applicability traces back to the requirements it chose to address.
Practiced in Lesson 1 · foundations and the case-study scope
6.3
New requirement
Planning of changes
What changed
A new sub-clause requires the organization to plan changes to the ISMS in a planned manner, considering the purpose of the changes and their potential consequences.
Clause 6.1 (risk assessment, risk treatment and the Statement of Applicability) is otherwise unchanged in structure.
What it means for the auditor
When you sample a change to the ISMS — a new system, a new supplier, a restructured team — trace how the organization planned it, rather than just accepting that it happened.
Also verify that risk assessment and risk treatment results still justify the current Statement of Applicability after the change.
Practiced in Lessons 2–3 · audit planning and Annex A sampling
8.1
Strengthened
Operational planning and control tightened
What changed
Clause 8.1 now explicitly requires the organization to establish criteria for its processes and to implement control of those processes in accordance with the criteria.
It also calls out controlling planned changes and reviewing the consequences of unintended changes, taking action to mitigate adverse effects where necessary.
What it means for the auditor
Ask for the criteria behind a process, not only the process itself, and follow one planned change and one unintended change through to how each was reviewed.
Practiced in Lesson 3 · conducting the audit and gathering objective evidence
10
Clarified
Continual improvement now comes first
What changed
The order of clause 10 is reversed: 10.1 is now Continual improvement and 10.2 is Nonconformity and corrective action, swapping the 2013 sequence.
The substance of the requirements is essentially unchanged.
What it means for the auditor
Update checklist references if you carried them over from the 2013 edition, and keep distinguishing correction from corrective action when you write findings.
Practiced in Lesson 4 · findings, grading and nonconformity reporting
A
Restructured
Annex A: 93 controls in 4 themes, not 114 in 14 clauses
What changed
Annex A moved from 14 clauses and 114 controls (2013) to 4 theme groups and 93 controls (2022): organizational, people, physical and technological controls.
Several 2013 controls were merged or consolidated, and 11 new controls were added — including threat intelligence, cloud security, ICT readiness for business continuity, physical security monitoring, configuration management, information deletion, data masking, data leakage prevention, monitoring activities, web filtering and secure coding.
What it means for the auditor
Audit the Statement of Applicability against the new theme structure, and sample a mix of legacy and newly added controls — a Statement of Applicability that has not been re-justified against the 93-control set is itself a common finding.
Remember that Annex A control selection always traces back to the risk assessment and risk treatment plan; a control cannot be "included" or "excluded" without a documented reason.
Practiced in Lesson 3 · risk-based sampling of Annex A controls
Route finder
Which ISO 27001 course do I need?
Already trained or working in information security auditing? First answer two questions, and then we will point you to the right next step — this 3FOLD advisory team can talk you through options we don't list on this page.
Question 1 of 2
Have you completed a CQI IRCA certified ISO/IEC 27001 ISMS Lead Auditor (or Auditor) training course?
What do you need from the training?
Our recommendation
Talk to an advisor about your CQI IRCA membership status.
You already hold a CQI IRCA certified ISO/IEC 27001:2022 ISMS Lead Auditor certificate. Whether you need to repeat any training depends on your current CQI IRCA membership grade and how recently you completed the course. Our advisors can check this with you directly, rather than guess from a general rule.
You need this CQI IRCA certified ISO/IEC 27001:2022 Lead Auditor course.
Your Lead Auditor training was on ISO/IEC 27001:2013 or earlier. Therefore, for ISMS Auditor grade membership you must complete the full CQI IRCA certified Lead Auditor course on the current edition. This 40-hour ISO 27001 Lead Auditor training covers ISO/IEC 27001:2022 throughout.
You need this CQI IRCA certified ISO/IEC 27001:2022 Lead Auditor course.
CQI IRCA auditor membership requires a CQI IRCA certified auditor or lead auditor course. This 40-hour ISO 27001 Lead Auditor training satisfies the training requirement for initial certification as an IRCA ISMS auditor.
This ISO 27001 Lead Auditor course is exactly what you need.
It builds the practical skills to plan, conduct, report and follow up ISMS audits — internal, supplier or third-party — through a full audit simulation, not just theory.
Tell an advisor what you're trying to achieve — a certification, a skill, or a specific project — and they will point you to the right option, on this page or otherwise.
What you will learn in the ISO/IEC 27001:2022 ISMS Lead Auditor online course
This ISO 27001 Lead Auditor training follows one audit from start to finish. The plan you write early is the plan you audit against later. Similarly, the findings you record are the ones you report at the end.
Lesson 1 · 1Sessions 1–3
Foundations of ISO/IEC 27001:2022 ISMS auditing
You will build a solid foundation in the ISO/IEC 27001:2022 ISMS standard and the ISO 19011 auditing guidelines — what an ISMS is and why organizations operate one, the clause structure (4–10), Annex A and the Statement of Applicability, the types of audit and the audit process. You will meet the realistic case-study auditee, initiate the audit, and begin reviewing documented information for a Stage 1 audit, with hands-on activities and a Q&A to consolidate your foundation.
Exam domains 1 and 2
1Determining which ISO/IEC 27001:2022 requirements apply to the case-study scope
2Reviewing the case-study organization's Statement of Applicability against its risk assessment
3Reviewing documented information for a Stage 1 audit and reporting readiness for Stage 2
Lesson 2 · 2Sessions 4–5
ISO/IEC 27001:2022 audit planning & preparation through ISO 19011
You will judge the readiness of the ISMS from the Stage 1 review, then prepare a risk-based Stage 2 audit plan, build an audit checklist and sampling plan, and prepare effective opening meetings. Through role-play you will simulate audit activities, exploring the organization's context, interested parties and information security risk, before a review discussion to reinforce your planning skills.
Exam domain 3
4Preparing a risk-based Stage 2 audit plan for the case-study organization
5Preparing the Stage 2 audit checklist and sampling plan against ISO/IEC 27001:2022
6Conducting the opening meeting as audit team leader (role-play)
Lesson 3 · 3Sessions 6–7
Conducting the audit & gathering objective evidence
The focus shifts to conducting the Stage 2 audit. You will practice interviewing, following audit trails and corroborating evidence, and audit the ISMS requirements across clauses 4–10 and a risk-based sample of Annex A controls — including risk assessment and treatment, the Statement of Applicability, access control, cryptography, supplier and cloud security, and incident management — through hands-on simulation and discussion.
Exam domain 4
7Auditing risk assessment, risk treatment and the Statement of Applicability (clause 6)
8Auditing a risk-based sample of Annex A controls (access control, cryptography, supplier & cloud security)
9Auditing incident management, logging and monitoring against Annex A
10Auditing operation, monitoring, internal audit and management review (clauses 8–9)
Lesson 4 · 4Sessions 8–10
Audit findings, grading & nonconformity reporting
A practice-rich lesson: you will evaluate evidence to determine conformity and nonconformity, grade findings as major or minor with justification, and write clear, accurate nonconformity reports using the three-part structure. You will also form the audit conclusions and structure the audit report, with practice questions to reinforce your findings and reporting skills.
Exam domain 5
11Writing and grading nonconformity reports from your audit evidence
12Forming audit conclusions and structuring the certification audit report
Lesson 5 · 5Sessions 11–13
Finalising the audit — closing, reporting & follow-up
The lesson opens with a full course review, then covers the closing meeting, presenting conclusions and recommendations, and post-audit activities — evaluating corrective action, root-cause analysis and audit follow-up in line with ISO 19011. It concludes with exam preparation and guidance on your CQI IRCA examination and IRCA registration.
Exam domain 5
13Presenting audit conclusions and recommendations to the auditee at the closing meeting (role-play)
14Evaluating corrective action responses: correction versus corrective action and root-cause analysis
From enrollment to Certificate of Achievement
EnrollPay online in AED or USD. Then we contact you within 24 hours.
Prepare on the LMSSelf-paced ISMS Foundation module and readiness quiz before the first session.
40 hours liveFive Sundays or 13 weekday evenings on Zoom, built around one audit simulation.
Sit the exam onlineDemo portal first, then the CQI IRCA exam within 30 days of the course.
Get your resultAfter that, CQI IRCA releases results in up to 15 working days.
CertificateFinally, your digital Certificate of Achievement arrives within 3 working days of passing.
Interactive · 2 minutes
Think like a lead auditor: spot the nonconformity
Eighty percent of this ISO 27001 Lead Auditor training is doing, rather than listening. For example, here are three situations from a certification audit against ISO/IEC 27001:2022. No sign-up, no score saved.
In the live course, these become full role-plays in Zoom breakout rooms. In addition, your trainer plays the auditee and gives written feedback on every activity.
Audit evidence notesFinding 1 of 3
Evidence · Risk treatmentThe ISMS manager shows you a risk treatment plan listing 14 risks. Three are marked "treated by Annex A control" with no reference to which control, no owner and no target date. "We know which controls apply. We just haven't written it down yet."
Which requirement is this evidence most relevant to?
6.1.3 requires a documented risk treatment plan and a Statement of Applicability with justifications. A risk marked "treated" without a named control, owner or date is not yet a documented treatment plan — the SoA cannot show conformity to a control it cannot name.
Evidence · Access controlYou sample 10 leavers from HR records over the last quarter. Eight had their system access revoked within 24 hours. Two — both from the same department — still had active accounts 3 weeks after their last working day.
Which nonconformity statement would stand up at the closing meeting?
Requirement, evidence, nature of the nonconformity. A defensible finding states all three and nothing more. Generalizing beyond the sample, unsupported claims and consultancy advice all fail. In the course, you write and grade real nonconformity reports from your own audit evidence.
Evidence · Incident managementDuring the audit of the incident log, you find three "low severity" phishing incidents in the last six months with no recorded root cause and no link to the security awareness training records for the affected team.
What should the auditor do next?
A pattern is a lead, rather than a finding. Incident management and lessons-learned controls in Annex A expect a link between incidents and root cause, including awareness gaps. Verify the evidence — the training records and the incident procedure — before you conclude.
Audit complete
0/3
You will practice this kind of thinking for 40 hours. In addition, you get a full case study, working documents and a trainer who pushes back.
Our ISO/IEC 27001:2022 ISMS Lead Auditor course is designed to accommodate busy professionals through flexible online learning. All times are Gulf Standard Time (GST).
5 Sundays · 9:00 am – 5:00 pm GST
Weekend batch (Sundays)
Attend live virtual classes every Sunday from 9:00 am to 5:00 pm GST for five weeks. This batch is ideal when you prefer to focus intensively on weekends.
7:00 pm – 10:00 pm GST
Weekday evening batch
A weekday evening format is enrolling now, with dates to be announced. Enquire below to be notified as soon as a batch is confirmed.
Your dates · your team
Corporate training
We schedule a dedicated batch around your team's availability, online or in-house. In addition, we tune the audit simulation to your sector.
Live on Zoom, with breakout roomsTrainer-led sessions, group exercises and audit role-plays that replicate a real audit team.
Nearpod interactive lessonsLive polls, quizzes and activities keep every session hands-on. No download needed.
3FOLD LMS — 3-month accessSelf-paced ISMS Foundation course, pre-course modules, case study and class recordings at 3foldlearn.com.
Editable audit working documentsCase studies, class templates, module slides and practice activities with model solutions.
Exam preparation zoneOfficial sample questions, three full mock exams with video reviews, and homework quizzes aligned with ISO 19011.
Quick turnaroundCertificate of Achievement within 3 working days of passing the continuous evaluation and final exam.
CQI IRCA exam
CQI IRCA exam structure, pass mark and procedure
The CQI IRCA exam for ISO 27001 Lead Auditor training has 40 questions worth 80 marks across five domains. To pass, you need at least 50% overall (40 of 80). In addition, you need the minimum mark in every domain. You sit this open-book exam online within 30 days of the course, and it lasts 1 hour 45 minutes.
+30min
English is not your first language? 3FOLD automatically adds 30 extra minutes to your CQI IRCA exam, giving you 2 hours 15 minutes instead of 1 hour 45. Also, you do not need to apply for it.
Exam pass-mark simulator
Drag the sliders. The white line on each bar is the domain minimum. However, a strong total does not rescue a weak domain. Above all, Domain 4 carries 36 of the 80 marks.
D1D2D3D4 · Conducting the auditD5 · Reporting
Your simulated result
42/80
Not yet a pass
52% overall clears the 50% line, but Domain 4 is one mark below its minimum of 14.
Internet access, search engines or online resources
Mobile phones, smart watches, earphones or other devices
Dictionaries, blank paper, or unauthorized books and handouts
CQI IRCA may treat possession of unauthorized items during the exam as malpractice, even if you do not use them.
What happens after you complete the course
First, your trainer submits your continuous assessment results. Then we register you on the CQI IRCA Authorized Training Partner Portal, and you receive access to two platforms:
Demo exam portal — check your system and practice in the real test environment.
Final exam portal — then sit the official CQI IRCA exam at a time that suits you. You have 30 days from the final course day.
If you pass, you receive a digitally verifiable Certificate of Achievement via Accredible within 3 working days of the result. However, if you do not pass and choose not to resit, you receive a Certificate of Attendance instead. Note that only the Certificate of Achievement qualifies you to apply for CQI IRCA auditor grades.
CQI IRCA exam attempts and fee structure
Attempt
Condition
Fee
Notes
1st
Included in the course fee
Free
Take it within 30 days of course completion. Missed attempts are marked "DNS" (Did Not Submit); no extensions.
2nd
Missed (DNS) or failed the 1st attempt
AED 125 / USD 35
Resit only, within one year of course completion. No need to re-attend the course.
3rd, 5th, 7th…
Failed the previous attempt — CQI IRCA requires course re-attendance
AED 310 / USD 85
Levy + exam fee. Re-attending the training is free within one year.
4th, 6th, 8th…
Resit after re-attending the course
AED 125 / USD 35
You receive a section-wise performance report after every attempt.
Schedule and fees
Upcoming ISO/IEC 27001:2022 ISMS Lead Auditor online training schedule
First choose your batch. Then pay in AED or USD to secure your seat in our CQI IRCA certified ISO 27001 Lead Auditor training.
After you pay. A member of the 3FOLD team contacts you within 24 hours with your detailed course schedule, Zoom joining instructions and access to all learning resources.
Use the right email. All future communication, including joining links and exam access, is sent to the email address you provide during payment. Therefore, check it before you pay. Telr handles the secure online payment.
Not sure where to start? We'll guide you.
Leave your details, and then an advisor will call you back with batch options.
Training a team of auditors?
Get group pricing and a dedicated ISO 27001 Lead Auditor training batch that fits around your team.
It is a CQI IRCA certified training course that gives you the knowledge and skills to plan, conduct, report and follow up first-, second- and third-party audits of an information security management system (ISMS) against ISO/IEC 27001:2022, in accordance with ISO 19011.
Is the ISO 27001 Lead Auditor course CQI IRCA approved?
Yes. 3FOLD Training is a CQI IRCA Approved Training Partner and this ISO/IEC 27001:2022 ISMS Lead Auditor course is certified by CQI and IRCA, UK (Course Approval No. PR373). You can also verify 3FOLD on the CQI IRCA training partner directory.
How long is the ISO/IEC 27001 Lead Auditor course and how is it delivered?
It is a 40-hour course delivered 100% online (Virtual Instructor-Led Training) as a 5-Sunday weekend batch (9:00 AM–5:00 PM GST). A weekday evening batch (13 sessions, 7:00 PM–10:00 PM GST) is also enrolling, with dates to be confirmed.
Do I need prior knowledge before the ISO/IEC 27001 Lead Auditor course?
Yes — the course assumes a working knowledge of information security management and ISO/IEC 27001. You complete a short self-paced ISMS Foundation module and readiness quiz on our LMS before the live sessions begin.
What certificate will I receive from the ISO/IEC 27001 Lead Auditor course?
Learners who pass the continuous assessment and the CQI IRCA examination receive a Certificate of Achievement; those who attend but do not pass receive a Certificate of Attendance. Only the Certificate of Achievement qualifies you to apply for CQI IRCA auditor membership.
How is the CQI IRCA exam structured and what is the pass mark?
The exam has 40 questions worth 80 marks across five domains. You must score at least 50% overall (40/80) and reach the minimum mark in every domain — 3 of 8 in each of domains 1 to 3, 14 of 36 in domain 4 (conducting the audit) and 8 of 20 in domain 5. It is taken online within 30 days of the course; duration is 1 hour 45 minutes, extended to 2 hours 15 minutes for non-native English speakers (3FOLD applies this automatically).
Is the ISO 27001 exam open book?
Yes. You may use your course notes and a clean copy of the ISO standards. Internet access and unauthorized items are strictly prohibited and treated as malpractice.
Who should attend the ISO 27001 Lead Auditor course?
Information security, IT, risk, GRC and compliance professionals; internal auditors and management-system professionals moving into ISMS auditing; consultants; and anyone pursuing IRCA ISMS auditor certification.
What happens if I fail or miss the ISO 27001 exam?
You can resit. A second attempt costs AED 125 / USD 35, and you can take it within one year without re-attending the course. However, if you do not pass the second attempt, CQI IRCA requires you to re-attend the course before trying again. Re-attendance at 3FOLD is free within one year; the levy plus exam fee for that attempt is AED 310 / USD 85.
How do I enroll in the ISO 27001 Lead Auditor course?
Choose your batch in the schedule on this page and pay securely online in AED or USD. A member of the 3FOLD team then contacts you within 24 hours with your course schedule, Zoom joining instructions and LMS access. You can also reserve a seat or ask questions on WhatsApp at +971 50 481 9989.
Join CQI IRCA certified ISO 27001 Lead Auditor training from an approved partner, not just a course provider. Seats for the next Sunday weekend batch are limited and filling fast.